Glassfish
GlassFish installation, clustering, default ports and paths, fine-tuning, certificates and asadmin commands.
15 min read
References
- How To Install Glassfish 4.0 on Ubuntu 12.04.3
- Install Glassfish 4 on a Debian 8 VPS
- How To Determine java heap size From GC Logs
- Tuning Your Java VM
- Java Platform, HotSpot Virtual Machine Garbage Collection Tuning Guide
- What is Java Heap?
Prerequisites
- Debian
- Java
GlassFish is an open-source enterprise level application server with high reliability and performance, which can run any Java EE project.
Clustering
A cluster is a collection of GlassFish Server instances that work together as one logical entity. A cluster provides a runtime environment for one or more Java Platform, Enterprise Edition (Java EE) applications. A cluster provides high availability through failure protection, scalability, and load balancing.
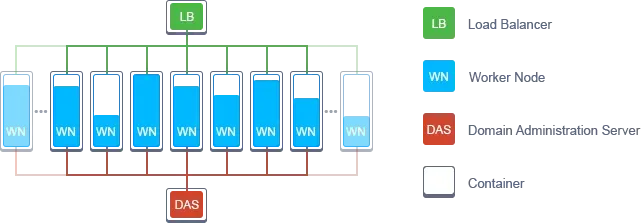
Install Glassfish
To download and install Glassfish application server
# Download Glassfish on Maven Central$ wget https://repo1.maven.org/maven2/org/glassfish/main/distributions/glassfish/5.1.0/glassfish-5.1.0.zip# Install unzip and then unzip Glassfish$ apt-get install unzip$ unzip glassfish-5.1.0.zip -d /optIn order to visit admin page (your_server_IP:4848) remotely, you need to enable secure admin not to get “Secure Admin must be enabled to access the DAS remotely” error
cd /opt/glassfish5/bin# Make the asadmin script executablechmod +x asadmin$ asadmin --host your_server_IP --port 4848 enable-secure-adminYou will receive the below error:
remote failure: At least one admin user has an empty password, which secure admin does not permit. Use the change-admin-password command or the admin console to create non-empty passwords for admin accounts.Command enable-secure-admin failed.If it is failed as above, change admin password first (default: username admin, password empty)
$ asadmin --port 15123 change-admin-passwordNow run this command again:
$ asadmin --host your_server_IP --port 4848 enable-secure-adminYou must restart all running servers for the change in secure admin to take effect.
$ asadmin restart-domain domain1To change port from 8080 to 80, edit
nano /opt/glassfish5/glassfish/domains/domain1/config/domain.xmlchange port to 80
<network-listener protocol="http-listener-1" port="8080"To change application context root, edit
nano /opt/glassfish5/glassfish/domains/domain1/config/domain.xmlchange context-root to /
<application context-root="/application"Configuration Reference
Default Port Assignments
| Default Ports | Listener description |
|---|---|
| 4848 | Administration Console (also for Admin and Monitoring REST interfaces) |
| 8080 | HTTP |
| 8181 | HTTPS |
| 8686 | JMX service |
| 3700 | IIOP |
| 3820 | IIOP/SSL |
| 3920 | IIOP/SSL with mutual authentication |
| 22 | SSH port |
| 9009 | Java debugger |
| 7676 | JMS provider |
| Auto-generated from the operating system’s dynamic port range | Message Queue TCP port |
| Auto-generated from the operating system’s dynamic port range | Message Queue Admin port |
| 9090 | GMS TCP start port |
| 9200 | GMS TCP end port |
| Auto-generated between GMS TCP start and end ports | GMS listener port |
| Auto generated between 2048 and 49151 | GMS multicast port |
Default Paths And File Names
| Placeholder | Value |
|---|---|
| as-install | user’s-home-directory/glassfish7/glassfish |
| as-install-parent | user’s-home-directory/glassfish7 |
| domain-root-dir | as-install/domains/ |
| domain-dir | domain-root-dir/domain-name |
| instance-dir | domain-dir/instance-name |
Default Administration Values
| Description | Default Value or Location |
|---|---|
| Domain name | domain1 |
| Master password | changeit |
| asadmin command-line utility | as-install/bin/asadmin |
| Configuration files | domain-dir/config |
| Log files | domain-dir/logs |
Fine-tuning
Read more
Display a list of command-line options that are passed to the Java application launcher when GlassFish Server is started.
asadmin list-jvm-optionsTo change jvm options, edit
nano /opt/glassfish5/glassfish/domains/domain1/config/domain.xmlLists the instrumented HotSpot Java Virtual Machines. Get pid just like ps in linux.
jpsPrints a histogram of the heap.
jmap -histo:live <pid>Prints a heap summary.
jmap -heap <pid>Guidelines for Calculating Java Heap Sizing
| Space | Command Line Option | Occupancy Factor |
|---|---|---|
| Java heap | -Xms and -Xmx | 3x to 4x old generation space occupancy after full garbage collection |
| Permanent Generation | -XX:PermSize -XX:MaxPermSize | 1.2x to 1.5x permanent generation space occupancy after full garbage collection |
| Young Generation | -Xmn | 1x to 1.5x old generation space occupancy after full garbage collection |
| Old Generation | Implied from overall Java heap size minus the young generation size | 2x to 3x old generation space occupancy after full garbage collection |
As a sample
- Having 2GB RAM => -Xms512m -Xmx1024m -XX:CompileThreshold=8000 -XX:PermSize=256m -XX:MaxPermSize=512m
- Having 8GB RAM => -Xms2048m -Xmx4096m -XX:CompileThreshold=8000 -XX:PermSize=1024m -XX:MaxPermSize=2048m
Install certificates
This will go into detail on how to install certificates on GLASSFISH Server.
- CREATE DIRECTORY FOR THE KEYSTORE AND CSR:
Open a command prompt and type the following:
mkdir sslcertThen cd to the newly created directory by typing the following command:
cd sslcert- CREATE KEYSTORE:
Use the following command to create a keystore:
keytool -genkey -alias youralias -keyalg RSA -keystore yourkeystorename.jks -keysize 2048You will be prompted to enter keystore password. The default password that comes with glassfish is changeit except you have changed yours. Afterwards, you will be prompted for the following:
Ensure the details filled in here correspond to those communicated at the point of purchasing,
What is your first and last name? = Your Domain Name (e.g. www.xyz.com)What is the name of your organizational unit? = Your Department (e.g. IT)What is the name of your organization? = Your Organization (e.g. XYZ CA Ltd)What is the name of your City or Locality? = Your City (e.g. Clifton)What is the name of your State or Province? = Your State (e.g. New Jersey)What is the two-letter country code for this unit? = Your Country Code (e.g. US)When all these have been filled in, you will be shown the summary to confirm accuracy. Type y and press enter. You will then be prompted to enter the key password for youralias. Press enter if you are using the default password.
- GENERATE CSR:
Use the following command to generate a CSR
keytool -certreq -alias youralias -file yourcsrname.csr -keystore yourkeystorename.jksNote: Use the same alias name you used for generating the keystore.
- IMPORT ROOT CERTIFICATE TO
cacerts.jksANDkeystore.jks:
keytool -import -v -trustcacerts -alias root -file addtrustexternalcaroot.crt -keystore keystore.jks- IMPORT INTERMEDIATE CERTIFICATE TO
cacerts.jksANDkeystore.jks:
keytool -import -v -trustcacerts -alias XYZRSAAddTrustCA -file XYZRSAAddTrustCA.crt -keystore keystore.jkskeytool -import -v -trustcacerts -alias XYZRSADomainValidationSecureServerCA -file XYZRSADomainValidationSecureServerCA.crt -keystore keystore.jksNote: Use a Unique alias name for each intermediate certificate.
- IMPORT MAIN CERTIFICATE TO
keystore.jks(THE ALIAS SHOULD BE SAME AS THAT OF THE KEYSTORE):
keytool -import -alias youralias -trustcacerts -file your_domain_certificate.crt -keystore keystore.jksYou should you should receive a message (Certificate reply was installed in keystore) if successful. It should NOT match the output of Step 1 or 2 above.
- CONFIGURE HTTP-LISTENER-2:
On the Glassfish Admin console, go to Configurations -> Server Config -> http-listener-2 and:
- Under the General tab, change the port from 8181 to 443
- Under the SSL tab, change the Certificate NickName from s1as to the alias of the main certificate (youralias) (which should be the same as the keystore alias)
- Save
- REFERENCE INSTALLED CERTIFICATE IN THE DOMAIN.XML:
Open the /config/domain.xml and replace all references of s1as with the alias of the installed certificate (youralias).
Commands
change-master-password
Each asadmin command accepts argument –passwordfile to instruct it to read all the necessary passwords from it to avoid asking for passwords interactively. But it’s a bit tricky to find out how to define passwords in this password file, because it’s used for multiple types of passwords.
- admin password with prefix
AS_ADMIN_PASSWORD, default is empty password - master password with prefix
AS_ADMIN_MASTERPASSWORD, default is “changeit” - user password with prefix
AS_ADMIN_USERPASSWORD - alias password with prefix
AS_ADMIN_ALIASPASSWORD
The default master password is changeit. You may want to change it by following command:
asadmin change-master-password --savemasterpassword=true mydomainUsing --savemasterpassword=true will save the password to the disk so that asadmin start-domain command doesn’t prompt for password. If you don’t want to store the password, omit this option.
Starting, Stopping, Restarting
$ asadmin start-domain$ asadmin stop-domain$ asadmin restart-domainAdding Resources
$ asadmin add-resources "/path/to/glassfish-resources.xml"Creating AuthRealm
$ asadmin create-auth-realm --classname realm_class [--help] [--property(name=value)[:name=value]*][--target target_name] auth_realm_nameDuring the creation of AuthRealm, if you get “remote failure: Creation of Authrealm jdbcbid failed.”, it turns out that the problem was locale language of JVM. After adding the following properties to JVM Options in Glassfish, everything will begin to work properly.
$ asadmin create-jvm-options -Duser.language=en$ asadmin create-jvm-options -Duser.region=USThen restart server to apply changes.
Deploying, Undeploying
$ asadmin deploy "/path/to/[application-name].war"$ asadmin undeploy [application-name]To prevent password entry each time
In order to save typing “admin username” and “password” every time you deploy or undeploy an application, create a password file pwdfile with content:
AS_ADMIN_PASSWORD=your_admin_passwordAdd —passwordfile in command:
$ asadmin --passwordfile pwdfile deploy /path/to/[application-name].warNow the prompt for username/password won’t appear.
Recover Glassfish admin password
changeit
admin;{SSHA256}dvCEGFNHGtSyXIhJvwR5FnviH+u8fCadrUIqp6uJc1tP9Bv10CGT7A==;asadminempty
admin;{SSHA256}2GiTMM0n4ulpMfRaMPMImYvVF522XY6nW2cKSXoY1EoM2QlHrHUkDQ==;asadminGlassfish mail-resource for domain, gmail and yandex using no-ssl, ssl, tls
Domain settings with no-ssl
<mail-resource jndi-name="mail/myMailSession" host="mail.domain.com" user="user@domain.com" from="user@domain.com" object-type="user" store-protocol="imap" store-protocol-class="com.sun.mail.imap.IMAPStore" transport-protocol="smtp" transport-protocol-class="com.sun.mail.smtp.SMTPTransport" debug="true" enabled="true"> <property name="mail.smtp.auth" value="true"/> <property name="mail.smtp.port" value="587"/> <property name="mail.smtp.password" value="PASSWORD"/> <property name="mail.smtp.starttls.enable" value="false"/></mail-resource>Gmail settings with SMTP Relay, SMTP Authentication and TLS encryption using an App Password
- Enable 2-Step Verification: Gmail account > Security
- Generate an App Password: Gmail account > Security > 2-Step Verification > App Passwords
- Your app password should be something like this;
abcd efgh ijkl mnop. Remove the whitespaces when using it.
<mail-resource jndi-name="mail/myMailSession" host="smtp-relay.gmail.com" user="user@gmail.com" from="user@gmail.com" enabled="true"> <property name="mail.smtp.auth" value="true"/> <property name="mail.smtp.starttls.enable" value="true"/> <property name="mail.smtp.port" value="587"/> <property name="mail.smtp.password" value="abcdefghijklmnop"/></mail-resource>Gmail settings with ssl
<mail-resource jndi-name="mail/myMailSession" host="smtp.gmail.com" user="user@gmail.com" from="user@gmail.com" object-type="user" store-protocol="imaps" store-protocol-class="com.sun.mail.imap.IMAPSSLStore" transport-protocol="smtps" transport-protocol-class="com.sun.mail.smtp.SMTPSSLTransport" debug="true" enabled="true"> <property name="mail.smtps.auth" value="true"/> <property name="mail.smtps.password" value="PASSWORD"/></mail-resource>Yandex settings with ssl
<mail-resource jndi-name="mail/myMailSession"               host="smtp.yandex.com"               user="user@domain.com"               from="user@domain.com"               object-type="user"               store-protocol="imaps"               store-protocol-class="com.sun.mail.imap.IMAPSSLStore"               transport-protocol="smtp"               transport-protocol-class="com.sun.mail.smtp.SMTPTransport"               debug="true"               enabled="true">    <property name="mail.smtp.auth" value="true"/>    <property name="mail.smtp.starttls.enable" value="true"/>    <property name="mail.smtp.port" value="587"/>    <property name="mail.smtp.password" value="PASSWORD"/>    <!-- It trusts the server anyway for the SSL connection. Host name or * for all -->    <property name="mail.smtp.ssl.trust" value="smtp.yandex.com"/>
    <property name="mail.imaps.auth" value="true"/>    <property name="mail.imaps.starttls.enable" value="false"/>    <property name="mail.imaps.host" value="imap.yandex.com"/>    <property name="mail.imaps.port" value="993"/>    <property name="mail.imaps.password" value="PASSWORD"/>    <!-- It trusts the server anyway for the SSL connection. Host name or * for all -->    <property name="mail.imaps.ssl.trust" value="*"/></mail-resource>
alternatedocroot example
glassfish-web.xml
<property description="Uploaded images" name="alternatedocroot_1" value="from=/images/* dir=/Users/[username]/Developments/backup"/>xhtml file
<p:graphicImage value="/images/logo.png"/>Note: Be sure that there is “/Users/[username]/Developments/backup/images” directory Note: use “value” attribute, not “name” attribute
JDBC connection pool and datasource
cp $HOME/mysql-connector-java-5.1.5-bin.jar $GLASSFISH_HOME/domains/domain1/lib/ext
$GLASSFISH_HOME/bin/asadmin create-jdbc-connection-pool --datasourceclassname com.mysql.jdbc.jdbc2.optional.MysqlDataSource --property user=root:password=test:DatabaseName=test:ServerName=localhost:port=3306 test-pool
$GLASSFISH_HOME/bin/asadmin create-jdbc-resource --connectionpoolid test-pool jdbc/test
To create a connection pool that supports distributed transaction, use com.mysql.jdbc.jdbc2.optional.MysqlXADataSource as datasourceclassname, and set --restype javax.sql.XADataSource option:
$GLASSFISH_HOME/bin/asadmin create-jdbc-connection-pool --restype javax.sql.XADataSource --datasourceclassname com.mysql.jdbc.jdbc2.optional.MysqlXADataSource --property user=root:password=test:DatabaseName=test:ServerName=localhost:port=3306 test-poolRun asadmin ping-connection-pool test-pool to verify whether the created connection pool can connect to the database. The database server needs to be running.
Configurations
According to the Glassfish Documentation, you can basically use server-config.
The default-config configuration is a special configuration that acts as a template for creating named configurations. Clusters and instances cannot refer to the default-config configuration. The default-config configuration can only be copied to create configurations.
So, below commands makes the same changes.
$ [GLASSFISH_HOME]/bin/asadmin create-jvm-options -Xmx=4g$ [GLASSFISH_HOME]/bin/asadmin create-jvm-options --target server-config -- '-Xmx4096m'Performance
Refer the documentation Optimize GlassFish Performance in a Production Environment
HTTP Compression
Edit [GLASSFISH_HOME]/glassfish/domains/domain1/config/domain.xml and change http-listener-1 and http-listener-2 under server-config configuration.
<configs> <config name="server-config">... <network-config> <protocols> <protocol name="http-listener-1"> <http max-connections="250" default-virtual-server="server" compression="on" compression-min-size-bytes="128" compressable-mime-type="text/html,text/css,text/plain,text/xml,application/javascript,application/json"> <file-cache></file-cache> </http> <ssl></ssl> </protocol> <protocol name="http-listener-2" security-enabled="true"> <http max-connections="250" default-virtual-server="server" compression="on" compression-min-size-bytes="128" compressable-mime-type="text/html,text/css,text/plain,text/xml,application/javascript,application/json"> <file-cache></file-cache> </http> <ssl classname="com.sun.enterprise.security.ssl.GlassfishSSLImpl" cert-nickname="s1as"></ssl> </protocol>Set/configure the EJB Timer Service’s DataSource
Database setup
Create the table EJB__TIMER__TBL from [GLASSFISH_HOME]/glassfish/lib/install/databases/ejbtimer_[DB_ENGINE].sql. DB_ENGINE is MySQL for example.
CREATE TABLE EJB__TIMER__TBL ( `CREATIONTIMERAW` BIGINT NOT NULL, `BLOB` BLOB, `TIMERID` VARCHAR(255) NOT NULL, `CONTAINERID` BIGINT NOT NULL, `OWNERID` VARCHAR(255) NULL, `STATE` INTEGER NOT NULL, `PKHASHCODE` INTEGER NOT NULL, `INTERVALDURATION` BIGINT NOT NULL, `INITIALEXPIRATIONRAW` BIGINT NOT NULL, `LASTEXPIRATIONRAW` BIGINT NOT NULL, `SCHEDULE` VARCHAR(255) NULL, `APPLICATIONID` BIGINT NOT NULL, CONSTRAINT `PK_EJB__TIMER__TBL` PRIMARY KEY (`TIMERID`));Server configuration
- Start your GlassFish server admin console: usually http://localhost:4848
- On your left navigate to [Configurations] > [server-config] > [EJB Container]
- Then click the TAB up top [EJB Timer Service]
- Then fill out Timer Datasource: with your JDBC Resource eg. [mysql-pu]. ( Note: Defaults to jdbc/__TimerPool)
- Restart the Server
The result
...INFO: [TimerBeanContainer] Created TimerBeanContainer: TimerBeanINFO: EJB5181:Portable JNDI names for EJB TimerBean: [java:global/ejb-timer-service-app/TimerBean, java:global/ejb-timer-service-app/TimerBean!com.sun.ejb.containers.TimerLocal]INFO: WEB0671: Loading application [ejb-timer-service-app] at [/ejb-timer-service-app]INFO: EJB5109:EJB Timer Service started successfully for data source [mysql-pu]INFO: Setting DBReadBeforeTimeout to falseINFO: ==> Restoring Timers ...INFO: There are no EJB Timers owned by this serverINFO: <== ... Timers Restored....Still Broken? TimerService just stopped working (it used to work)?
So this happened to me after a day full of “deploy on save”. The TimerService was unavailable all of a sudden.
Severe: Exception while loading the appSevere: Undeployment failed for context /ejb-timer-service-appWarning: Cannot deploy or load EJBTimerService: org.glassfish.deployment.common.DeploymentException: Error in linking security policy for ejb-timer-service-app -- Inconsistent Module StateSolution:
- Stop the Glassfish server
- Delete all the content from
{GLASSFISH_HOME}/glassfish/domains/yourdomainname/generated - Restart Glassfish
It works, but everytime I need to deploy I need to follow this procedure again.
Useful links
Realm
BASIC
- Go to http://localhost:4848 and login as admin to Admin interface.
- Go to Security -> Realms -> File
- Add a group name (Administrators:Members) to Assign Groups field.
- Open manage users at the top of the page.
- Click New and add an user (testuser) and give a password.
- Add
Administrators:Membersto the Group List. (Separate multiple groups with colon) - Put the below lines to
glassfish-web.xmlandweb.xml.
glassfish-web.xml
<glassfish-web-app> <security-role-mapping> <role-name>Administrator</role-name> <group-name>Administrators</group-name> </security-role-mapping> <security-role-mapping> <role-name>Member</role-name> <group-name>Members</group-name> </security-role-mapping></glassfish-web-app>web.xml
<web-app> <security-constraint> <web-resource-collection> <web-resource-name>Administrator Area</web-resource-name> <url-pattern>/administrator/*</url-pattern> </web-resource-collection> <auth-constraint> <role-name>Administrator</role-name> </auth-constraint> </security-constraint> <security-constraint> <web-resource-collection> <web-resource-name>Member Area</web-resource-name> <url-pattern>/member/*</url-pattern> </web-resource-collection> <auth-constraint> <role-name>Member</role-name> </auth-constraint> </security-constraint> <login-config> <auth-method>BASIC</auth-method> <realm-name>file</realm-name> </login-config> <security-role> <role-name>Administrator</role-name> </security-role> <security-role> <role-name>Member</role-name> </security-role></web-app>Errors
Out-of-Memory exception
By changing the -Xmx JVM options in GLASSFISH_HOME/domains/domain1/config/domain.xml will solve the problem. Default value is <jvm-options>-Xmx512m</jvm-options>, set a higher value like <jvm-options>-Xmx1024m</jvm-options> instead.
If you have already done that or if it doesn’t resolve the OutOfMemoryError, then try and get a heap dump when the OOME occurs, then analyze it. To get a heap dump, add in domain.xml the following option: <jvm-options>-XX:+HeapDumpOnOutOfMemoryError</jvm-options>. This will cause Glassfish to generate a heap dump file with a .hprof extension. Once you have this file, you can analyze it with a tool such as Eclipse Memory Analyzer Tool to find out which object allocation is causing the JVM to throw an OOME.
software.amazon.awssdk.core.exception.SdkClientException: Unable to execute HTTP request: sun.security.validator.ValidatorException: PKIX path building failed: sun.security.provider.certpath.SunCertPathBuilderException: unable to find valid certification path to requested target
- Amazon AWS Server Authentication
- SunCertPathBuilderException: unable to find valid certification path to requested target
- Let’s Encrypt. Glassfish. AWS EC2.
- Root certificates for Stripe domains
- amazon trust services
Solution1:
MailSSLSocketFactory sf = new MailSSLSocketFactory();sf.setTrustAllHosts(true);properties.put("mail.imap.ssl.trust", "*");properties.put("mail.imap.ssl.trust", "imap.yandex.com");properties.put("mail.imap.ssl.socketFactory", sf);properties.put("mail.smtp.ssl.trust", "*");properties.put("mail.smtp.ssl.trust", "smtp.yandex.com");properties.put("mail.smtp.ssl.socketFactory", sf);Solution2:
- openssl s_client -connect server:port -showcerts
- copy the text from cert you want into a file
- keytool -import -trustcacerts -file [-keystore mystore]
Example:
Grab the server certificate and save it to yourcert.pem file
openssl s_client -showcerts -connect sns.eu-west-1.amazonaws.com:443or directly save it to yourcert.pem file
echo | openssl s_client -connect yoursever:port 2>&1 | sed -ne '/-BEGIN CERTIFICATE-/,/-END CERTIFICATE-/p' > yourcert.pemCopy the text from cert you want into a file. In this example name it as yourcert.pem
Import root and intermediate certificates to the trusted root certificate
For JAVA
sudo keytool -import -alias <server_name> -keystore $JAVA_HOME/lib/security/cacerts -file yourcert.pem -storepass changeitFor GlassFish
keytool -import -alias <server_name> -keystore ${GLASSFISH_HOME}/glassfish/domains/domain1/config/cacerts.jks -file <server_name>.cert -storepass changeitAnd restart the GlassFish server.
Other useful commands
#To Delete a Certificate by Using keytoolsudo keytool -delete -noprompt -alias aws -keystore $JAVA_HOME/lib/security/cacerts -storepass changeit#To get list of certificateskeytool -list -keystore $JAVA_HOME/lib/security/cacerts -storepass changeit > list.txtkeytool -v -list -keystore ${GLASSFISH_HOME}/glassfish/domains/domain1/config/keystore.jks > list.txtjava.lang.NoSuchMethodError: sun.security.ssl.Handshaker.setApplicationProtocols([Ljava/lang/String;)V
The problem is that Glassfish embeds an old version of the SUN implementation (sun.security.ssl.SSLSessionImpl). Removing it will resolve the problem.
$ cd ${GLASSFISH_HOME}/glassfish/modules/endorsed#View the content of grizzly-npn-bootstrap.jar$ jar -tf grizzly-npn-bootstrap.jar#Remove "sun" directory and all directories under it from grizzly-npn-bootstrap.jar$ zip -d grizzly-npn-bootstrap.jar sun\*other commands to remove a file or a folder
#Remove a file from a jar$ zip -d file.jar unwanted_file.txt#Remove a directory from a jar$ zip -d file.jar unwanted_folder/TLS ALPN (Application-Layer Protocol Negotiation) support is not available. HTTP/2 support will not be enabled.
Error generating artifacts for the following WSDL []. Possible causes can be invoking https when the application is not configured for security.
When try to go to the local SOAP URL both ?WSDL and ?Tester links work fine.
When go to the remote SOAP URL (JAX-WS) ?WSDL link works, but ?Tester is not due to this error.
The problem is caused by the default setting restricting access to External Schema. By default in IDE we use -Djavax.xml.accessExternalSchema=all as vmArg in IDE’s settings or in maven pom file.
If you are deploying to the GlassFish Server you need to modify the configuration file of the GlassFish Server (domain.xml) to enable the server to access external schemas to parse the wsdl file and generate the test client. To enable access to external schemas, open the GlassFish configuration file (GLASSFISH_INSTALL/glassfish/domains/domain1/config/domain.xml) and add the following JVM option element. You will need to restart the server for the change to take effect.
</java-config> ... <jvm-options>-Djavax.xml.accessExternalSchema=all</jvm-options></java-config>Connection could not be allocated because: Cannot open file:GLASSFISH_HOME/glassfish/domains/domain1/config/keystore.jks
Add allowPublicKeyRetrieval=true and useSSL=false in GlassFish Admin Console JDBC > JDBC Connection Pools > Additional Properties.
or add them to glassfish-resources.xml
<jdbc-connection-pool ... <property name="allowPublicKeyRetrieval" value="true"/> <property name="useSSL" value="false"/></jdbc-connection-pool>or import certificate into glassfish and change the master password. In domain.xml, the following 2 lines needed to be added in the jvm-options area.
<jvm-options>-Djavax.net.ssl.keyStorePassword=[password]</jvm-options><jvm-options>-Djavax.net.ssl.trustStorePassword=[password]</jvm-options>The Master Password is required to start the domain. No console, no prompting possible. You should either create the domain with —savemasterpassword=true or provide a password file with the —passwordfile option. Command start-domain failed.
This error occurs after running glassfish image on docker compose.